Your SSL certificate now expires faster. Here is what to do about it
SSL certificates are capped at 200 days, then 100, then 47. See who is affected, who is not, and a 60-second check you can run today.
On this page
The short answer
Since 15 March 2026, publicly trusted SSL/TLS certificates can last at most 200 days. The limit falls to 100 days on 15 March 2027 and to 47 days on 15 March 2029. If your host issues and renews certificates automatically, you will notice little. If you install certificates by hand, you will be renewing about eight times a year, often more, by 2029, so move to automatic renewal.
The Saturday morning problem
Picture a Saturday morning. A customer taps the link in your Instagram bio and lands on a full-screen browser warning, something like "Your connection is not private." She does not read the small print. She closes the tab and buys from someone else.
Nothing was hacked. No server crashed. A small file reached its expiry date and nobody renewed it.
That file is an SSL certificate, and it is about to expire more often, by design. Whether that matters to you depends on one question, and you can answer it in about a minute. First, the facts.
What changed, and when
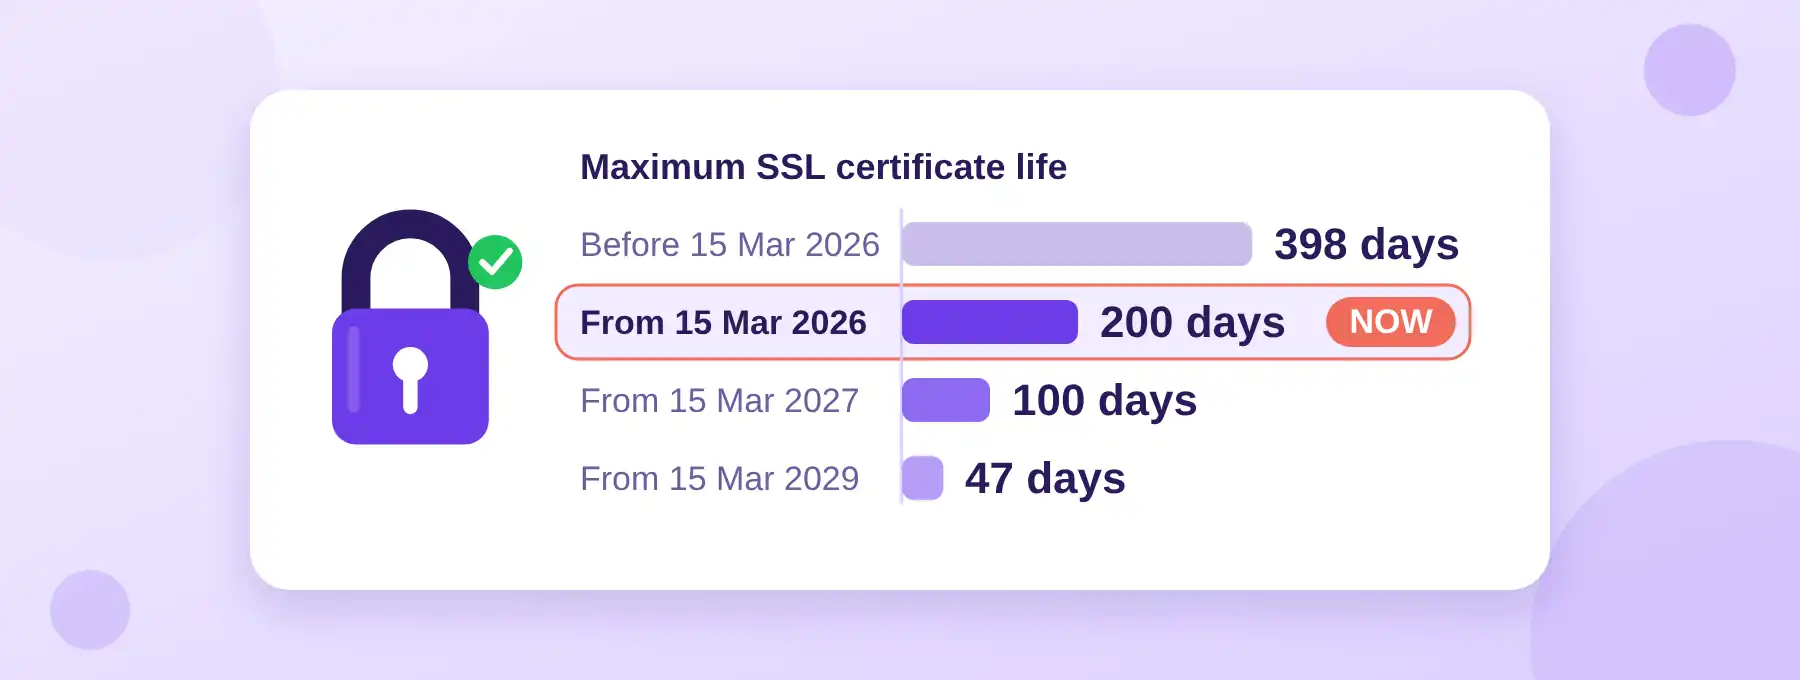
Every publicly trusted SSL/TLS certificate has a maximum lifetime. The limit is set by the CA/Browser Forum, the group where certificate authorities and browser makers agree on the rules. In April 2025 its members approved a schedule that cuts that lifetime in steps:
- Before 15 March 2026: up to 398 days
- From 15 March 2026: up to 200 days (this is where we are now)
- From 15 March 2027: up to 100 days
- From 15 March 2029: up to 47 days
The new limit applies to certificates issued on or after each date. A certificate you already hold keeps its expiry date, so the change reaches you the next time you renew.
One more detail matters later. By 2029, a certificate authority may reuse its proof that you control your domain for only 10 days. Proving ownership becomes a routine, repeated step instead of a one-off.
Why shorter is safer
If a certificate's private key leaks, whoever holds it can pose as your site until the certificate expires. Under the old 398-day limit, a stolen key could stay useful for more than a year. At 47 days, that window drops to under seven weeks.
Think of it as changing the lock on your front door every few weeks instead of once a year. Tedious if you do it by hand. Invisible if a machine does it.
Are you affected? It depends on who renews
The automatic group. Your host or control panel issues a free certificate and renews it quietly in the background. You have probably never thought about it, and that is the goal. At the time of writing, our own shared hosting plans at Hostlelo list free SSL that is issued and renewed for you. Let's Encrypt, a free certificate authority many sites use, is also shortening its own lifetimes on a published timeline: an opt-in 45-day option since May 2026, a 64-day default from February 2027, and 45 days from February 2028.
The manual group. You bought a certificate, received a file, and installed it yourself, or a developer did. Count what that means. At 200 days you renew almost twice a year. At 100 days it is nearly four times. At 47 days it is about eight, and often more, because renewals usually happen before the old certificate runs out.
Each renewal is a chance to forget, and a forgotten renewal looks exactly like the Saturday morning story. A reminder in one person's calendar does not scale to eight a year, especially when that person goes on holiday.
The 60-second check
You can find out which group you are in right now.
- Open your site in a browser and click the padlock or site information icon beside the address bar.
- Open the certificate details. The menu names change between browser versions, but you are looking for the "valid to" or "expires on" date.
- Read the date. If it is months away, nothing is urgent today.
- Ask who issues and renews it: your host, a plugin, or a person on your team.
- If the answer is "a person, by hand", ask your host whether they can switch you to automatic renewal.
If you are still setting things up, our guide to redirecting HTTP traffic to HTTPS with .htaccess covers the step that comes right after the certificate is installed.
Two questions for your host
Two questions tell you almost everything.
- Who issues and renews my certificate, and how often?
- If a renewal fails, who gets the alert, and how fast can you fix it?
A good answer is specific. "It renews automatically every few weeks, and we email you if it ever fails" beats "don't worry about it." If you are comparing providers, our checklist for choosing a UAE hosting company turns questions like these into a buying process.
The one message worth forwarding
Send this to whoever looks after your website:
"Who renews our SSL certificate, and what happens if that person is on leave?"
If the answer is "the host, automatically", you can stop thinking about it. If the answer is "a person, by hand", you have just found a small risk that is cheap to fix today and awkward to fix on a Saturday morning. Either way, you asked the question before the warning page asked it for you.
Reader questions
How long can an SSL certificate last in 2026?
Up to 200 days for certificates issued on or after 15 March 2026. Some authorities set the limit slightly lower. GlobalSign, for example, lists 199 days for its standard products.
When will SSL certificates last only 47 days?
On 15 March 2029, under the CA/Browser Forum schedule. The step before that is 100 days, starting 15 March 2027.
Do I need to replace my SSL certificate now?
No. A certificate you already have stays valid until its own expiry date. The shorter limit applies to certificates issued after each milestone, so you see it the next time you renew.
Will my host's free SSL still renew automatically?
If your host issues and renews the certificate for you, yes, that is what the automation is for. Ask your host how renewals work on your plan and what alert you receive if one fails.
Is Let's Encrypt changing its certificate lifetime too?
Yes. Its published timeline is an opt-in 45-day profile from May 2026, a 64-day default from February 2027, and a 45-day default from February 2028.
Sources & further reading
Originally published . Revised for this edition.